Cybersecurity
Governance: Structure & policy reviews
Maturity: Security baseline capability
ISO 27001: End-to-end audit readiness
Awareness: Executive security workshops
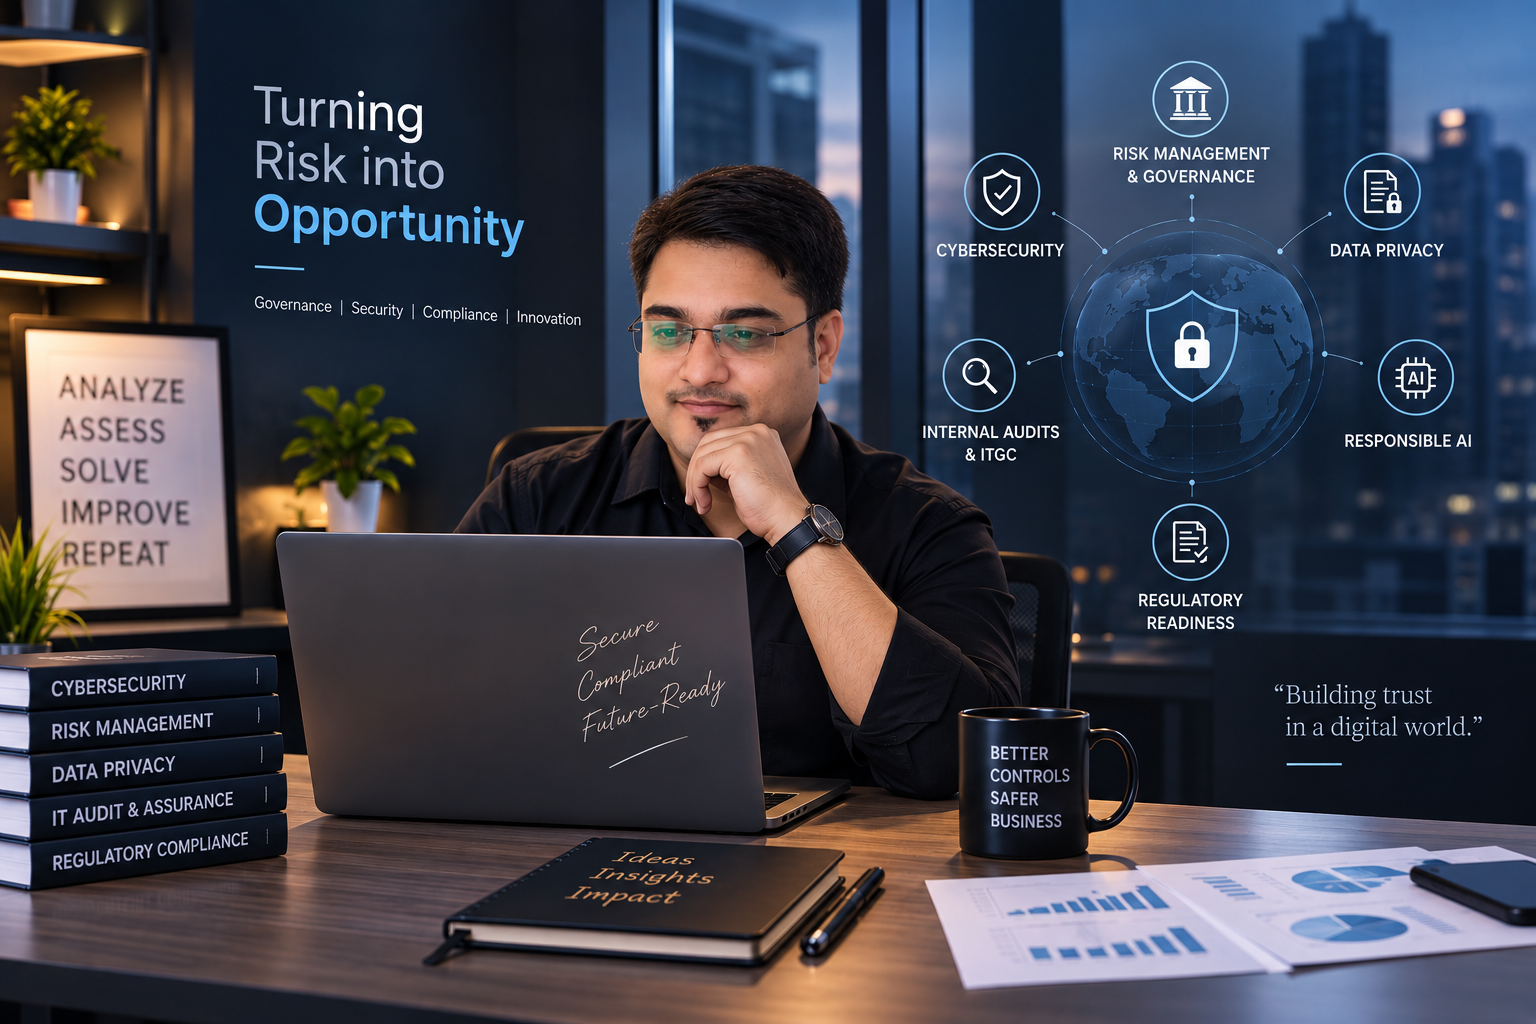
Enabling secure, compliant and future-ready organizations through risk-based strategies, responsible AI frameworks and robust governance.
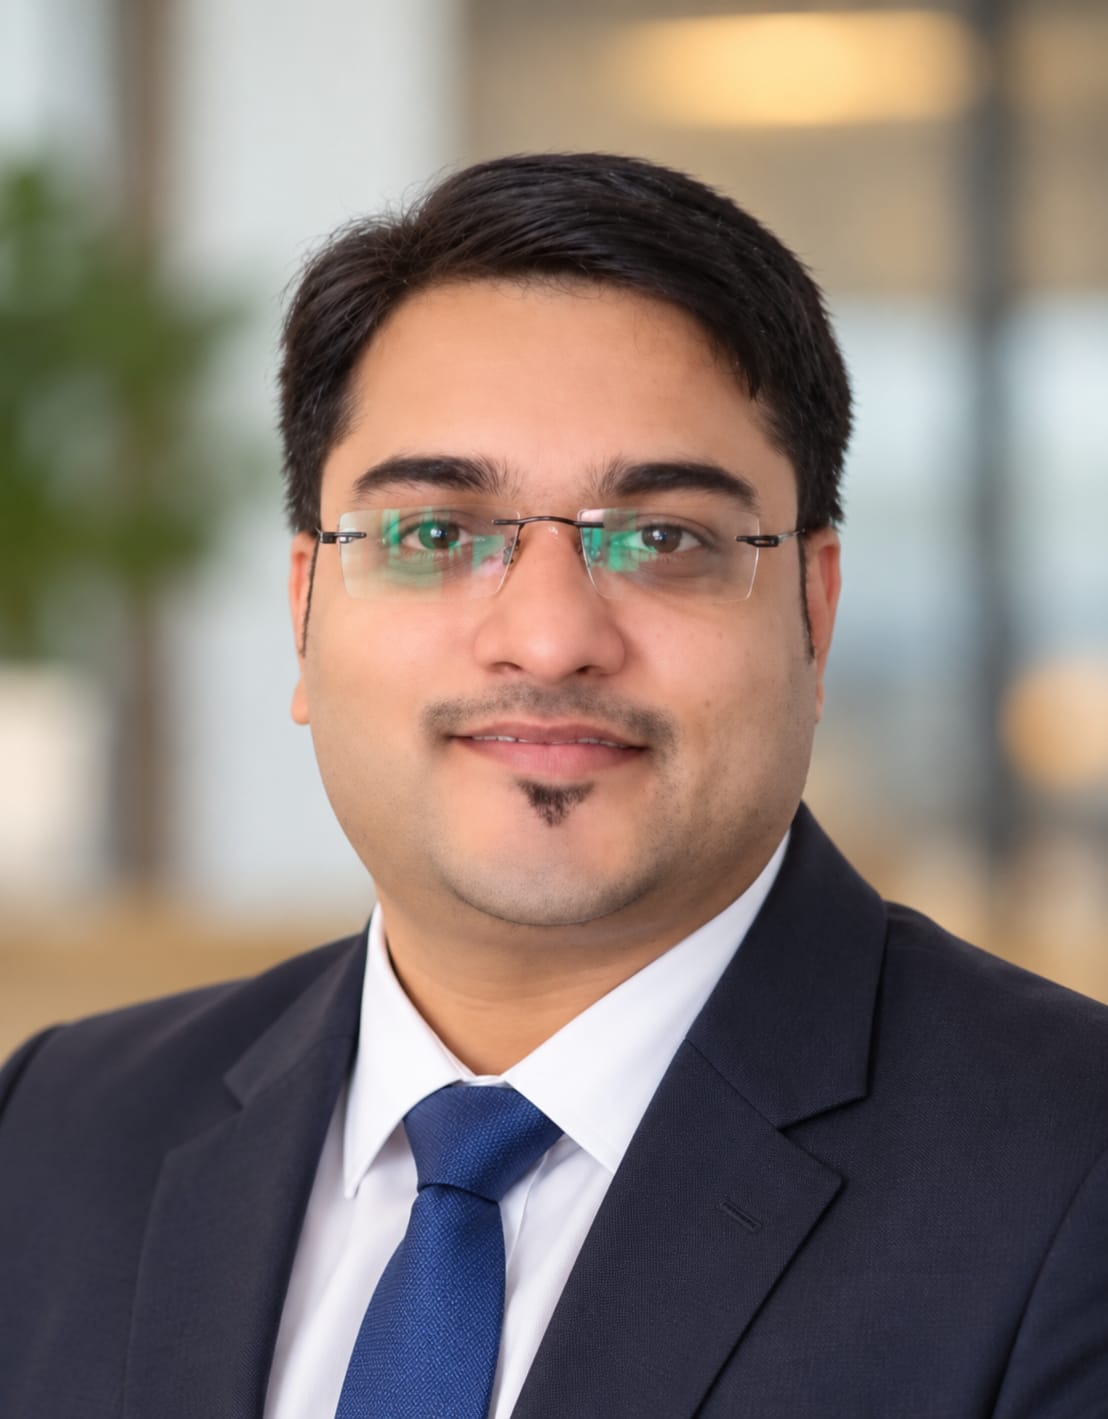
Strategic Governance, Risk & Assurance, Data Privacy & Security, Cybersecurity, Audit professional with 17+ years of experience.
Extensive experience in enterprise risk management, information security governance, regulatory compliance, DPDPA 2023, GDPR, ISO 27001, ISO 42001, TPRM, technology audit, AI Security and AI Governance Audits.
Partnered with global tech leaders and financial institutions to strengthen their governance across critical risk domains. I bring deep domain depth and adaptability across Banking & Financial Services, the Insurance Sector, Education Institutions, and NGOs & Non-Profits.
"My core mission is to empower enterprise boards and executive leadership to manage technology risks, assure AI governance, and achieve regulatory compliance."
Enabling organizations to embrace technology with confidence — balancing security, governance, privacy, and responsible innovation to build a resilient future
Governance: Structure & policy reviews
Maturity: Security baseline capability
ISO 27001: End-to-end audit readiness
Awareness: Executive security workshops
ITGC Reviews: General control evaluation
Internal Audit: IT risk focused reviews
Cyber Audit: Threat posture validation
Vendor Risk: Third-party risk assurance
ISO 42001: Management system setup
AI Risk Reviews: Model & data risk checks
Responsible AI: Ethics & bias controls
Frameworks: NIST AI RMF alignment
DPDPA Readiness: Indian privacy act strategy
GDPR Compliance: Global data privacy
Privacy Risk: DPIA & impact assessments
Control Reviews: Data life-cycle checks
Deep domain depth across banking, financial services, and global tech leaders.
Hands-on security background combined with executive audit experience.
Expert guidance on RBI, DPDPA, GDPR, PCI-DSS, and global ISO standard frameworks.
Pioneering capability in ISO 42001 AI governance and responsible AI assurance.
Board-ready reporting leveraging Power BI and Tableau visualization metrics.
ISACA Certified
Lead Auditor
AI Lead Auditor
Privacy Expert
ISACA Specialty
Recognized for excellence in technology risk management and AI governance adoption.
Lead strategic risk advisory, DPDPA and privacy compliance initiatives, technology assurance and governance activities.
Spearhead AI Security & Governance Audits, evaluating model lifecycles, explainability, risk management and ISO/IEC 42001 alignment.
Led multiple IT, Cyber Security, Network Security, BCM/DR, Third-Party Vendor, and IT Application audits, including gap assessments against RBI, DPDP, PCI-DSS, and other regulatory guidelines.
Led a 5-member audit team across planning, walkthroughs, risk assessments, reporting, and RBI submissions, while contributing to RBI regulatory initiatives and BCM/DR drills.
Spearheaded IT Infrastructure and Cyber Security Audits for a bank, covering audit planning, risk assessment, control testing, regulatory compliance, and reporting.
Reviewed key security controls, firewall rules, traffic, and proxy configurations to identify control gaps, anomalies, and security risks.
Built a strong foundation across technology infrastructure, network security, information security and enterprise technology operations, with experience spanning ITGC and internal controls, network deployment and modernization, firewall and security administration, vulnerability remediation, infrastructure governance, disaster recovery and technology support.
Privacy implementation programs for Kotak Mahindra Bank.
Cybersecurity awareness sessions for Mahesh Sahakari Bank Ltd. & Mahesh Professional Forum.
AI Governance and Security Audits covering model lifecycle, explainability, risk and responsible AI.
Supporting organizations with governance, privacy and regulatory readiness.
Risk-based strategies aligned with organizational objectives.
Actionable governance and assurance approaches designed for real-world environments.
Responsible AI, privacy and security frameworks designed for evolving regulatory expectations.
Gap analysis and roadmap for AI Management System certification.
Alignment with NIST AI Risk Management Framework (NIST AI RMF).
Ethics controls, model risk assessments, and executive awareness.
"Adopt AI confidently while managing governance, compliance, and risk."
"The cybersecurity awareness session was practical, engaging, and highly relevant to banking operations. Complex cybersecurity concepts were explained in a simple and actionable manner."
"Strong understanding of regulatory expectations, technology risks, and governance frameworks. Audit recommendations were realistic and helped strengthen our control environment."
"Excellent blend of technical expertise, compliance knowledge, and business understanding. The session provided valuable insights into AI governance and cybersecurity risks."
Project-Based: Targeted risk assessments, audits, and gap reviews.
Retainer Model: Ongoing monthly advisory, audit, & risk support.
Training Model: Custom workshops & awareness programs.